
The Essential GDPR Compliance Checklist for UK Business in 2026
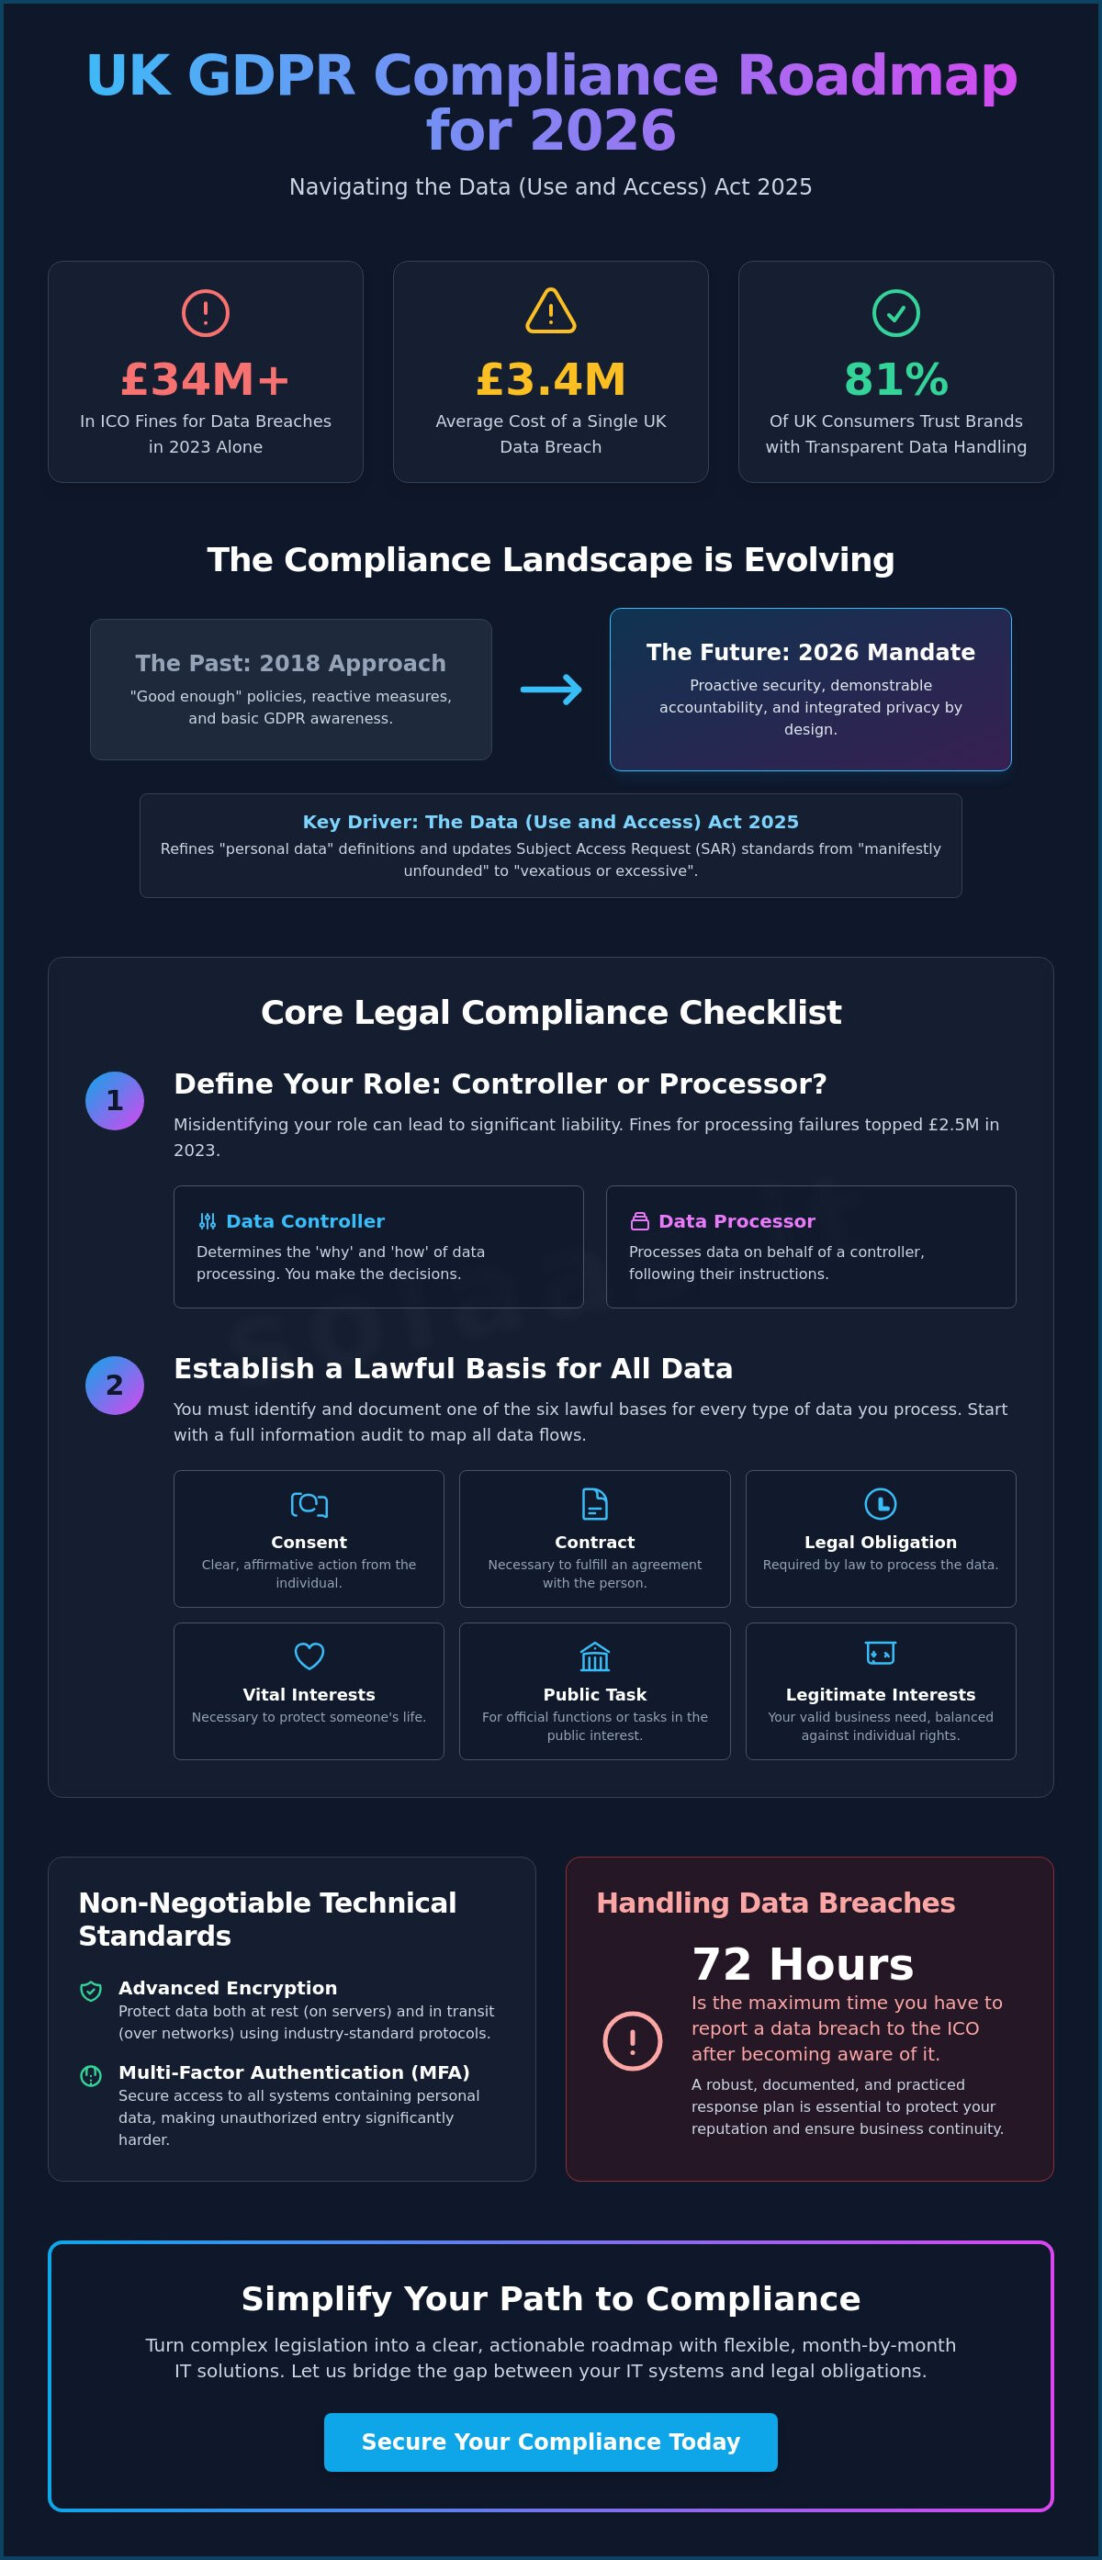
Did you know that the Information Commissioner’s Office (ICO) issued over £34 million in fines for data breaches in 2023 alone? It’s a staggering figure that highlights why staying ahead of regulations is no longer optional. As we move toward 2026, many UK directors feel overwhelmed by the complexities of the 2025 Data (Use and Access) Act and how it alters their existing responsibilities. You’ve likely felt the pressure of trying to align your technical infrastructure with shifting legal standards without losing operational speed. This gdpr compliance checklist for uk business is designed to eliminate that uncertainty and put the reins back in your hands.
We believe that compliance shouldn’t be a barrier to your success. You deserve a partner who turns complex legislation into a clear, actionable roadmap. This article provides a comprehensive, “done-for-you” style framework that bridges the gap between your IT systems and legal obligations. We’ll walk you through the essential technical audits, documentation updates, and scalable security measures you need to ensure your business remains resilient and fully compliant throughout 2026.
Key Takeaways
- Understand why 2018 standards are no longer sufficient and how to navigate the transition to the 2025 Data (Use and Access) Act requirements.
- Audit your legal foundations using our comprehensive gdpr compliance checklist for uk business to ensure every piece of data has a clear lawful basis.
- Identify the non-negotiable technical standards, including advanced encryption and Multi-Factor Authentication, required to secure a modern IT infrastructure.
- Master the 72-hour ICO reporting rule and develop a robust response plan to protect your reputation and operational continuity during a breach.
- Discover how flexible, month-by-month IT solutions can simplify your path to compliance without locking your business into rigid long-term contracts.
The 2026 UK Data Landscape: Why Compliance Has Changed
Welcome to a new era of IT where data isn’t just an asset; it’s a responsibility that defines your brand’s integrity. The regulatory environment has shifted dramatically since the original General Data Protection Regulation (GDPR) was first adopted. By 2026, the “good enough” approach of 2018 has become a major liability. The Information Commissioner’s Office (ICO) now prioritises proactive security and demonstrable accountability over simple policy documents. If your gdpr compliance checklist for uk business hasn’t been updated since the turn of the decade, your organisation is likely exposed to unnecessary risk.
Modern compliance isn’t about avoiding fines. It’s about building a scalable foundation for your company’s future. The ICO’s 2025-2026 strategic plan emphasizes that businesses must prove they’ve integrated privacy into their daily operations. This shift means that being reactive is no longer an option. You need a partner who understands that flexible, tailored solutions are the only way to stay ahead of these evolving requirements.
The Data (Use and Access) Act 2025
The introduction of the Data (Use and Access) Act 2025 marked the most significant change to UK data law since Brexit. This legislation refined the definition of “personal data” to provide more clarity for businesses operating in a high-tech environment. One of the most practical changes involves Subject Access Requests (SARs). The previous “manifestly unfounded or excessive” threshold was replaced with a “vexatious or excessive” standard. This allows your team to better manage resource-heavy requests that aren’t made for legitimate privacy reasons. Your 2026 data processing records must reflect these new legal definitions to ensure your gdpr compliance checklist for uk business remains accurate and effective.
Accountability as a Competitive Advantage
Smart leaders treat data privacy as a tool for success rather than a burden. A 2024 survey revealed that 81% of UK consumers feel more confident sharing information with companies that demonstrate transparent data handling. This transparency directly impacts your bottom line by increasing customer conversion rates. When you treat privacy as a core value, you’re not just ticking boxes; you’re building a reputation for reliability.
The cost of staying stagnant is high. With the average cost of a UK data breach reaching £3.4 million in recent industry reports, the ROI of managed security is undeniable. Investing in comprehensive, month-by-month security solutions allows you to scale safely. It puts the reins of your business growth firmly back in your hands, ensuring your brand remains untarnished in a competitive market.
Core GDPR Compliance Checklist: The Legal Essentials
Success in the digital economy requires more than just great services; it demands a foundation of trust and legal precision. Your first step in any gdpr compliance checklist for uk business is to define your role. You’re either a Data Controller, the entity that determines the purpose and means of processing, or a Data Processor, handling data on behalf of a controller. Misidentifying these roles can lead to significant liability; in fact, the ICO issued over £2.5 million in fines related to processing failures in 2023 alone. As your trusted partner, we ensure you have the clarity needed to operate with confidence.
Lawful Basis and Information Audits
You can’t protect data if you don’t know where it’s stored. Conduct a thorough information audit to map every data flow within your organisation. For every piece of information you collect, you must establish one of the six lawful bases:
- Consent: Clear, affirmative action from the individual.
- Contract: Necessary to fulfill a contract with the person.
- Legal Obligation: Required by law.
- Vital Interests: To protect someone’s life.
- Public Task: For official functions or public interest.
- Legitimate Interests: Your business has a valid reason that doesn’t override the individual’s rights.
If you use legitimate interests for your marketing efforts, you’re required to document a Legitimate Interests Assessment (LIA). This documentation proves you’ve balanced your business needs against the privacy of your clients. For detailed technical criteria, refer to the ICO’s Guide to GDPR to ensure your audit meets the highest standards of the gdpr compliance checklist for uk business.
Individual Rights and Transparency
By 2026, transparency standards will demand even greater clarity. Your Privacy Notice must be written in plain, jargon-free English so a non-expert can understand it instantly. It’s about empowering your customers, not hiding behind legal walls. You should also prepare for Subject Access Requests (SARs). These requests have increased by 40% in the UK since 2022, making a manual response process unsustainable for growing firms.
Managing the “Right to be Forgotten” is particularly challenging in modern infrastructures. When a client asks for their data to be deleted, you must ensure it’s removed from live databases and cloud backups alike. This is where a flexible and scalable IT partner becomes invaluable, providing the tools to manage data lifecycle tasks automatically. Finally, implement a strict Data Retention Policy. Data hoarding is a security risk; if you don’t need it for a specific business outcome, it shouldn’t be on your servers.
The Technical Checklist: Securing Your IT Infrastructure
Building a robust gdpr compliance checklist for uk business requires moving beyond policy documents into hard technical controls. In 2024, the Information Commissioner’s Office (ICO) emphasized that technical insecurity remains a leading cause of data breaches. You must ensure encryption is active at rest and in transit. This means using AES-256 for stored data and TLS 1.3 for data moving across networks. Without these, your business is exposed to intercept risks that lead to heavy fines. It’s a non-negotiable standard for any firm handling sensitive client details.
For financial professionals, adopting secure software from providers like Apex Tax Solutions LLC ensures that tax preparers can meet these rigorous encryption and security standards when managing sensitive client information.
Multi-Factor Authentication (MFA) is your first line of defence. Microsoft data shows that MFA blocks 99.9% of automated account attacks. Every cloud account in your organisation, from email to CRM, needs this enabled. It’s a simple step that provides unparalleled peace of mind. For remote teams, endpoint security is vital. With 44% of the UK workforce working in a hybrid capacity as of late 2023, managing laptops and mobiles via Mobile Device Management (MDM) ensures that lost devices can be wiped remotely before a breach occurs.
Data availability is a core pillar of GDPR. Your disaster recovery plan should include immutable backups. These prevent ransomware from encrypting your secondary data sets. Integrating a Forbes GDPR Checklist into your audit process helps verify that your technical recovery times align with the 72-hour breach reporting window required by UK law. If you don’t have a tested recovery path, you aren’t truly compliant.
Cloud Security and Telephony
Your communication tools are often the most overlooked part of a gdpr compliance checklist for uk business. Modern cloud phone systems must handle call recordings with care. You’re required to inform callers if you’re recording and provide a clear legal basis for doing so. VoIP traffic must be encrypted to prevent eavesdropping. SolaaS ensures your cloud providers use UK-based data centres, keeping your data within the jurisdiction of UK GDPR and avoiding complex international transfer rules. This keeps your connectivity seamless and your compliance airtight.
Access Control and Identity Management
The principle of Least Privilege (PoLP) ensures staff only access data essential for their role. This limits the “blast radius” if an account is compromised. Automating user offboarding is a critical security step. When an employee leaves, their access should vanish instantly. Leaving “zombie” accounts active for even 24 hours creates a massive security hole. Real-time monitoring for unauthorised access attempts allows your team to react to threats before they escalate into full-scale data disasters. We help you put the reins of your security firmly back in your hands.
Handling Data Breaches and Ongoing Maintenance
Compliance doesn’t end once you’ve mapped your data. It’s a living process that requires constant vigilance. Your gdpr compliance checklist for uk business must prioritize a robust Data Breach Response Plan. This document isn’t just a safety net; it’s a roadmap that identifies who does what when a security incident occurs. Assign clear roles to your IT lead, legal advisor, and Data Protection Officer (DPO) to ensure your team moves as one unit during a crisis.
The 72-hour rule is strict. It leaves no room for hesitation. You’ve got exactly 72 hours from becoming aware of a breach to report it to the Information Commissioner’s Office (ICO) if it poses a risk to individuals. Effective reporting requires having the facts ready: the nature of the breach, the types of data involved, and your immediate containment strategy. Don’t wait for a perfect picture; the ICO prefers early, partial reports over delayed ones.
Staff training is the human element of your security. Since human error contributed to 68% of data breaches according to recent industry findings, regular workshops keep security top-of-mind. Combine this with technical safeguards like monthly vulnerability scanning and quarterly penetration testing. These proactive measures find the holes in your perimeter before hackers can exploit them.
Reporting and Documentation
Your ICO report must include the approximate number of records affected and the contact details for your DPO. If a breach is likely to result in a high risk to people’s rights, you must inform them directly. Use clear, jargon-free language to explain what happened and what steps they should take, such as changing passwords. For minor incidents that don’t meet the reporting threshold, you must still maintain an internal breach log to demonstrate accountability during future audits.
Continuous Compliance Monitoring
Annual audits aren’t enough for 2026 standards. The pace of digital change means your risks shift every week. Forward-thinking firms are now automating compliance checks through managed IT support services to catch deviations instantly. This ensures your Data Protection Impact Assessments (DPIAs) stay updated whenever you introduce new software or change how you process customer information. It’s about moving from reactive fixes to a culture of continuous privacy.
Ready to secure your business and stay ahead of regulations? Partner with SolaaS for flexible IT solutions that put the reins of your security back in your hands.
Partnering for Compliance: How SolaaS Simplifies GDPR
Compliance isn’t a static goal; it’s a continuous commitment to your customers’ privacy. SolaaS provides the flexible IT infrastructure you need to tick every box on your gdpr compliance checklist for uk business. We believe technology should empower your growth, not tie you down with rigid, outdated agreements. That’s why we offer month-by-month options, putting the reins of your communication services firmly back in your hands. You get the support you need precisely when you need it, without the burden of long-term contracts.
Our approach focuses on proactive protection. Instead of reacting to a data breach after the damage is done, we implement systems that stop threats before they compromise your files. For SMEs and retail businesses, we provide specific expertise in UK GDPR, ensuring your operations remain lawful as regulations evolve toward 2026 standards. We bridge the gap between complex legal requirements and practical, daily IT operations.
Scalable Security for Growing Businesses
We build tailored IT roadmaps that treat compliance as a core pillar of your business strategy. For retail environments, our AI-driven solutions serve a dual purpose. They prevent physical theft through smart monitoring while simultaneously anonymising and protecting sensitive customer data. This ensures your security measures don’t accidentally become a privacy liability. If you’re still using legacy communication tools, we help you migrate to a secure, compliant cloud platform. This transition ensures every call, message, and file transfer meets the high encryption standards required by modern UK law.
- Tailored IT Roadmaps: We align your technology growth with 2026 compliance milestones.
- AI Retail Solutions: Smart systems that protect inventory and data privacy at the same time.
- Secure Cloud Comms: Move away from vulnerable on-site hardware to encrypted, compliant cloud environments.
Your Trusted Partner in Coventry and Beyond
While we have deep roots in Coventry, our team provides a national reach for businesses across the UK. You get direct access to a team of experts who understand the nuances of 2026 laws. We don’t just provide software; we act as a dedicated problem-solver for your specific business challenges. In 2023, the ICO handled thousands of data protection complaints, highlighting how easily businesses can slip up. We ensure you aren’t part of those statistics by providing clear, actionable guidance and robust technical safeguards.
Our goal is to make your business more efficient and cost-effective while maintaining an ironclad security posture. Whether you’re a local shop or a national enterprise, our scalable solutions grow with you. We’re ready to help you break free from the constraints of traditional IT providers and embrace a more agile, secure future.
Future-Proof Your Data Strategy for 2026
Navigating the UK’s evolving data landscape requires more than a one-time audit. As the Information Commissioner’s Office (ICO) increases its focus on AI-driven processing and automated decision-making in 2026, your infrastructure must be both resilient and transparent. This gdpr compliance checklist for uk business provides the essential framework to address legal essentials, technical vulnerabilities, and proactive maintenance. You’ve now got the tools to ensure your operations remain secure, lawful, and ready for whatever comes next.
Compliance shouldn’t be a barrier to your growth. SolaaS acts as your trusted partner, providing the expertise needed to manage complex regulations without the constraints of long-term contracts. We deliver tailored compliance roadmaps and expert UK-based support designed for the modern enterprise. By choosing a flexible approach to Managed IT, you put the reins of your security and connectivity firmly back in your hands. We focus on the technical details so you can focus on your productivity.
Secure your business with our flexible Managed IT Services
Your data is your most valuable asset. Let’s work together to protect it and empower your long-term success.
Frequently Asked Questions
Is my small UK business exempt from GDPR in 2026?
No small UK business is exempt from GDPR requirements in 2026 if it processes any personal data. While the Data (Use and Access) Act 2025 aims to reduce administrative burdens for low-risk activities, the fundamental principles of lawful processing and data rights remain mandatory for all 5.6 million UK small businesses. Your gdpr compliance checklist for uk business must include basic records of processing even if you’ve under 250 employees.
How long do I have to respond to a Subject Access Request (SAR)?
You must respond to a Subject Access Request within one month of receipt. This 30-day deadline is a strict legal requirement under the UK GDPR and the Data Protection Act 2018. If a request is particularly complex, you’ve the right to extend this by a further two months, but you must inform the individual about the delay and the reasons for it within the initial month.
What is the maximum fine for a UK GDPR breach in 2026?
The maximum fine for a serious UK GDPR breach in 2026 is £17.5 million or 4% of your total annual worldwide turnover, whichever is higher. For less severe infringements, the Information Commissioner’s Office (ICO) can issue fines up to £8.7 million or 2% of global turnover. These penalties ensure that data protection remains a boardroom priority for every scalable enterprise seeking a trusted partner status.
Do I need a Data Protection Officer (DPO) for my medium-sized business?
You don’t necessarily need a formal Data Protection Officer unless your core activities involve regular and systematic monitoring of individuals on a large scale. Under the Data (Use and Access) Act 2025, many businesses can now appoint a Senior Responsible Individual instead of a DPO. This tailored approach provides the flexibility your business needs to stay compliant while maintaining focus on your core productivity goals.
How does the Data (Use and Access) Act 2025 affect my current privacy policy?
The Data (Use and Access) Act 2025 streamlines your privacy policy by replacing prescriptive records of processing with more flexible management programs for low-risk data. It clarifies how scientific research and law enforcement data are handled. Update your gdpr compliance checklist for uk business to reflect these new definitions of identifiable information to ensure your policy stays modern and accurate.
Can I store UK customer data on servers located in the US?
Yes, you can store UK customer data on US servers provided you use the UK-US Data Bridge established in October 2023. This framework allows for the seamless transfer of personal data to certified US organisations without requiring a separate International Data Transfer Agreement. Always verify that your US cloud provider is on the approved list maintained by the US Department of Commerce to ensure a secure solution.
What are the technical requirements for “Privacy by Design”?
Privacy by Design requires technical measures like AES-256 encryption for data at rest and TLS 1.3 for data in transit. You should implement automated data minimisation protocols that delete records once their specific purpose expires. These robust solutions ensure your infrastructure is secure by default, putting the reins of data control back in your hands and protecting your customers’ trust.

Article by
René Wheeler
René Wheeler is Managing Director of SolaaS, bringing over three decades of experience in IT and telecoms. He is a strong advocate for transparency and flexibility, championing monthly contract models that allow businesses to stay agile and in control of their technology. His approach challenges traditional industry practices and puts client outcomes first